
The discovery of a concealed recording device at OpenAI highlights how competition over advanced artificial intelligence is turning proprietary research into a valuable target for corporate espionage and foreign intelligence operations.
OpenAI confronts the growing threat of corporate espionage
OpenAI confronts the growing threat of corporate espionage
By The Beiruter | October 19, 2026

Reading time: 4 min
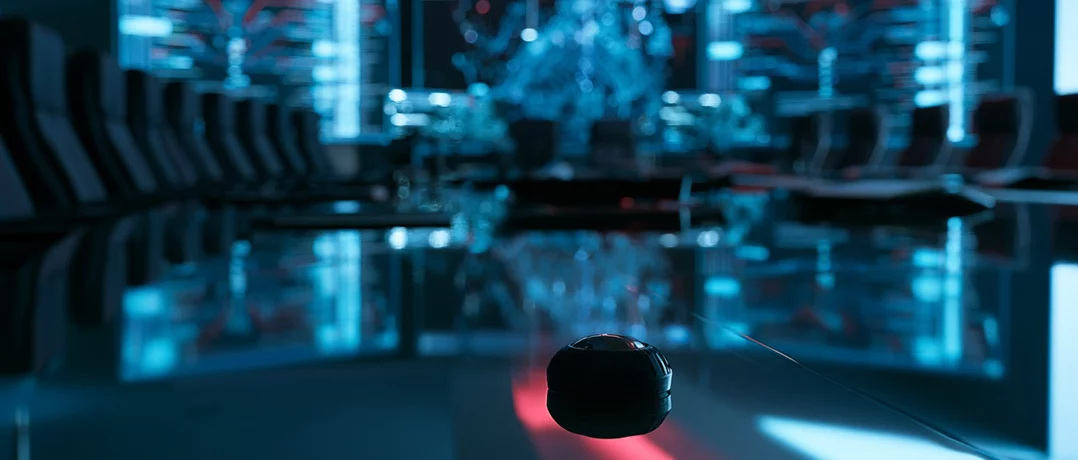
A recording device wrapped in toilet paper and concealed behind a television is an unlikely symbol of the technological competition surrounding artificial intelligence. Yet its discovery in October 2026 inside an executive conference room at OpenAI's San Francisco headquarters has exposed a vulnerability that even the industry's most sophisticated companies cannot easily eliminate. Federal prosecutors allege that Abdulrahman Alfozan, a 35-year-old Saudi engineer employed by OpenAI, planted the encrypted device after using AI tools to research meeting schedules and assist in its development. OpenAI says its own models subsequently helped investigators identify him. The FBI arrested Alfozan in October, although authorities have not established any foreign government involvement or reported the theft of proprietary models, source code or customer data. Advanced AI research has become a valuable target for commercial competitors and foreign intelligence services. In its June 2026 technology threat assessment, cybersecurity firm CrowdStrike identified China-linked groups as particularly active in targeting technology companies, attributing more than 58% of state-sponsored targeted intrusions against the sector in its dataset to these actors. Protecting AI intellectual property requires securing digital networks alongside employees, facilities and research processes. Corporate espionage, the covert acquisition of confidential business information for competitive advantage, has gained significance as AI becomes central to computing, manufacturing, finance and defense. Advanced AI systems require enormous investments in hardware, training data and research expertise. Their model weights, the numerical parameters developed during training, contain much of the resulting capability. Obtaining them could allow a competitor to reproduce valuable capabilities without undertaking the original development process. In its August 2026 report Achieving AI Model Weight Security Level 3, US-based research organization RAND estimated that frontier AI development had cost leading laboratories billions of dollars by 2025. The theft of model weights, researchers warned, could undermine commercial competitiveness while potentially transferring sensitive capabilities to malicious actors. The commercial value of these technologies was evident in the prosecution of former Google engineer Linwei Ding. In January 2026, a federal jury convicted him of stealing confidential AI technology, including information concerning Google's computing infrastructure. Prosecutors alleged that he transferred sensitive materials to a personal account while pursuing business interests in China. Although convicted of economic espionage, Ding subsequently had those counts overturned when a judge found insufficient evidence of an intended benefit to the Chinese government. For countries seeking to accelerate domestic AI development, access to proprietary research can offer substantial economic advantages. The same technology may also have military and intelligence applications, making certain commercial assets relevant to national security. The same technologies that companies are trying to protect are also becoming useful instruments for those seeking unauthorized access to them. Google's September 2026 threat intelligence findings documented a campaign in which an attacker used an AI coding chatbot and autonomous agents to plan and execute credential harvesting in less than six hours, compromising thousands of third-party credentials. In another operation, investigators discovered a system designed to manage more than 23,800 stolen credentials and other sensitive records, including those associated with cloud and AI services. The targets are geographically dispersed. Google identified China-linked activity against North American research institutions and separate theft and extortion operations targeting proprietary AI assets in North America and Europe. The affected industries included healthcare, technology and media, demonstrating that valuable AI research is no longer concentrated exclusively in specialized laboratories. If substantiated, the OpenAI allegations would demonstrate how readily available AI tools can facilitate traditional methods of intelligence gathering. Yet the distinction between suspected insider misconduct, commercial theft, and state-sponsored intelligence operations remains essential. The nationality of an accused employee does not establish a foreign intelligence connection, nor does unauthorized recording necessarily demonstrate an attempt to steal AI technology. For AI developers, stronger security presents a difficult institutional trade-off. Scientific progress depends on collaboration, access to computing resources and the exchange of technical knowledge, while commercial competition creates incentives to restrict precisely those activities. RAND proposed 262 security controls addressing 31 potential methods of stealing AI model weights, including compromised credentials, malicious insiders and unauthorized physical access. In a small workshop involving industry and government specialists, human intelligence threats attracted 78% of votes when participants identified their leading concerns, ahead of credential compromise at 44%. The findings are indicative rather than representative of the entire industry. The greatest implementation obstacles were organizational rather than technical. Participants rated additional costs and slower development at 4.3 out of five in severity, compared with 1.7 for shortages of AI security expertise. Companies are already adjusting their defenses. Anthropic activated its AI Safety Level 3 protections in May 2025, introducing stronger safeguards against the theft of model weights alongside measures intended to reduce the risks associated with more capable systems. The company nevertheless acknowledged the difficulty of defending against sophisticated insiders and well-resourced state actors. The implications reach well outside Silicon Valley. As governments and businesses across Asia, Europe and the Middle East invest in domestic AI capabilities, protecting research and infrastructure becomes a question of economic sovereignty as well as corporate competitiveness. OpenAI's investigation has not established that its technological secrets were compromised. Nevertheless, the discovery of a concealed recorder illustrates a persistent weakness in an industry built around extraordinarily advanced systems. Protecting artificial intelligence may ultimately depend as much on controlling ordinary human access as on developing more sophisticated technology.The value of an AI secret
Espionage in the age of AI
The challenge of securing innovation
-
-
-
The Beiruter
-
